Halo have removed this guide from their knowledge base. This is our last mirrored copy, kept so existing links keep working — it may now be out of date.
Configuring Intune App Protection (MAM) for the Halo Mobile applications
- Mobile App
- intune
- intune integration
- Intune App Protection
- MAM
- MDM
- MSAL
Halo version: v2.244+
Halo Mobile version: Halo mobile app (iOS & Android) - v1.5+
Audience: Halo administrators configuring Microsoft Intune protection for their organisation.
Last updated: 03/07/2026
1. Introduction
The Halo mobile app lets your agents connect to your Halo instance from a phone or tablet.
By default, sign-in uses the same method as the Halo web application, but can optionally be protected with Microsoft Intune App Protection so that Halo data on the device is PIN-gated and remotely wipeable.
There are two sign-in modes, chosen automatically based on your Halo settings:
| Mode | When | What the user gets |
|---|---|---|
| Standard SSO | Default. Intune App Protection not enabled. | Normal Halo or Entra (if web app SSO is configured) sign-in. Halo tokens stored securely on device. |
| Intune-protected | You enable Intune App Protection (MAM). | Entra sign-in via the Microsoft broker app, Intune enrolment, then Halo access - with App Protection policy applied. |
This guide covers everything needed to set up Intune-protected sign-in.
Prerequisites checklist
- Halo web app on version 2.244 or later.
- Halo mobile applications (iOS or Android) on version 1.5 or later.
- Halo mobile application enabled in your Halo instance.
- Microsoft Entra ID (Azure AD) tenant with an SSO app registration already configured for Halo. This must be configured in the "Single Sign-on" module.
- Halo Agents are synced with Microsoft Entra ID (Azure AD).
- For Intune features only: an Intune subscription (Plan 1 or a suite that includes it) and the appropriate admin roles.
- Admin who can grant tenant admin consent in Entra.
2. How it all fits together
Configuration happens in up to three places. The first two are required to enable sign-in with a Microsoft broker app. Intune configuration is optional, but MAM policies are recommended to allow enrolment with Intune.
1. Microsoft Entra ID (your Halo SSO app registration)
  - Expose an API
  - access_as_user
  - Authorise Halo Mobile
  - Grant admin consent

   ↓

2. Halo Configuration
  - Activate "Enable Intune App Protection (MAM) for the Mobile App" in Advanced Settings.
  - Pick a "Single Sign-On Configuration" record for the Mobile app to use for authentication in Advanced Settings.
  - Choose an Intune enrolment mode (required or optional) in Advanced Settings.

   ↓

3. Microsoft Intune (Optional)
  - MAM / App Protection Policies
  - Conditional Access
  - MDM
  - Managed Configuration
At sign-in, the app reads your instance's settings, and if Intune is enabled, it authenticates against your SSO app registration through the Microsoft broker, enrols the app with Intune, then exchanges that token for a Halo session.
If no broker app (Intune Company Portal on Android, Microsoft Authenticator on iOS) is installed on the device, then sign-in can still be completed but, Intune enrolment cannot be completed.
3. Choose what you need
| Your goal | Configure |
|---|---|
| Entra sign-in via the Microsoft broker app | Entra SSO (§4) + Halo settings (§5) |
| Protect Halo data on personal/BYOD devices | MAM - App Protection Policy (§7). Requires Entra steps §4 + Halo settings §5. |
| Force a device to be managed before access | MDM device enrolment + (optionally) Conditional Access (§8, §9). |
| Auto-connect the app to a fixed Halo URL on managed devices | MDM managed config halo_url (§8.3). |
| Guarantee protection is enforced, not just attempted | Conditional Access "Require app protection policy" (§9). |
Recommendation: use Conditional Access to enforce protection. Halo's "Intune enrolment mode = Required" (§5.3) is a convenient in-app fallback, but Intune Conditional Access is the robust, Microsoft-native enforcement point.
4. Microsoft Entra ID (Azure) configuration
These steps let the Halo mobile app use a native Microsoft broker app to request a token scoped to your SSO application, which Halo then validates and exchanges for a Halo session.
4.1 Prerequisite - Azure SSO already set up in Halo
Standard Entra SSO for Halo must already be working. The steps below modify that same SSO app registration.
To configure Single Sign-On with Entra in Halo this, please see the following guide;
Note that SSO must be configured in the Single Sign-on module - not the legacy Entra SSO settings.
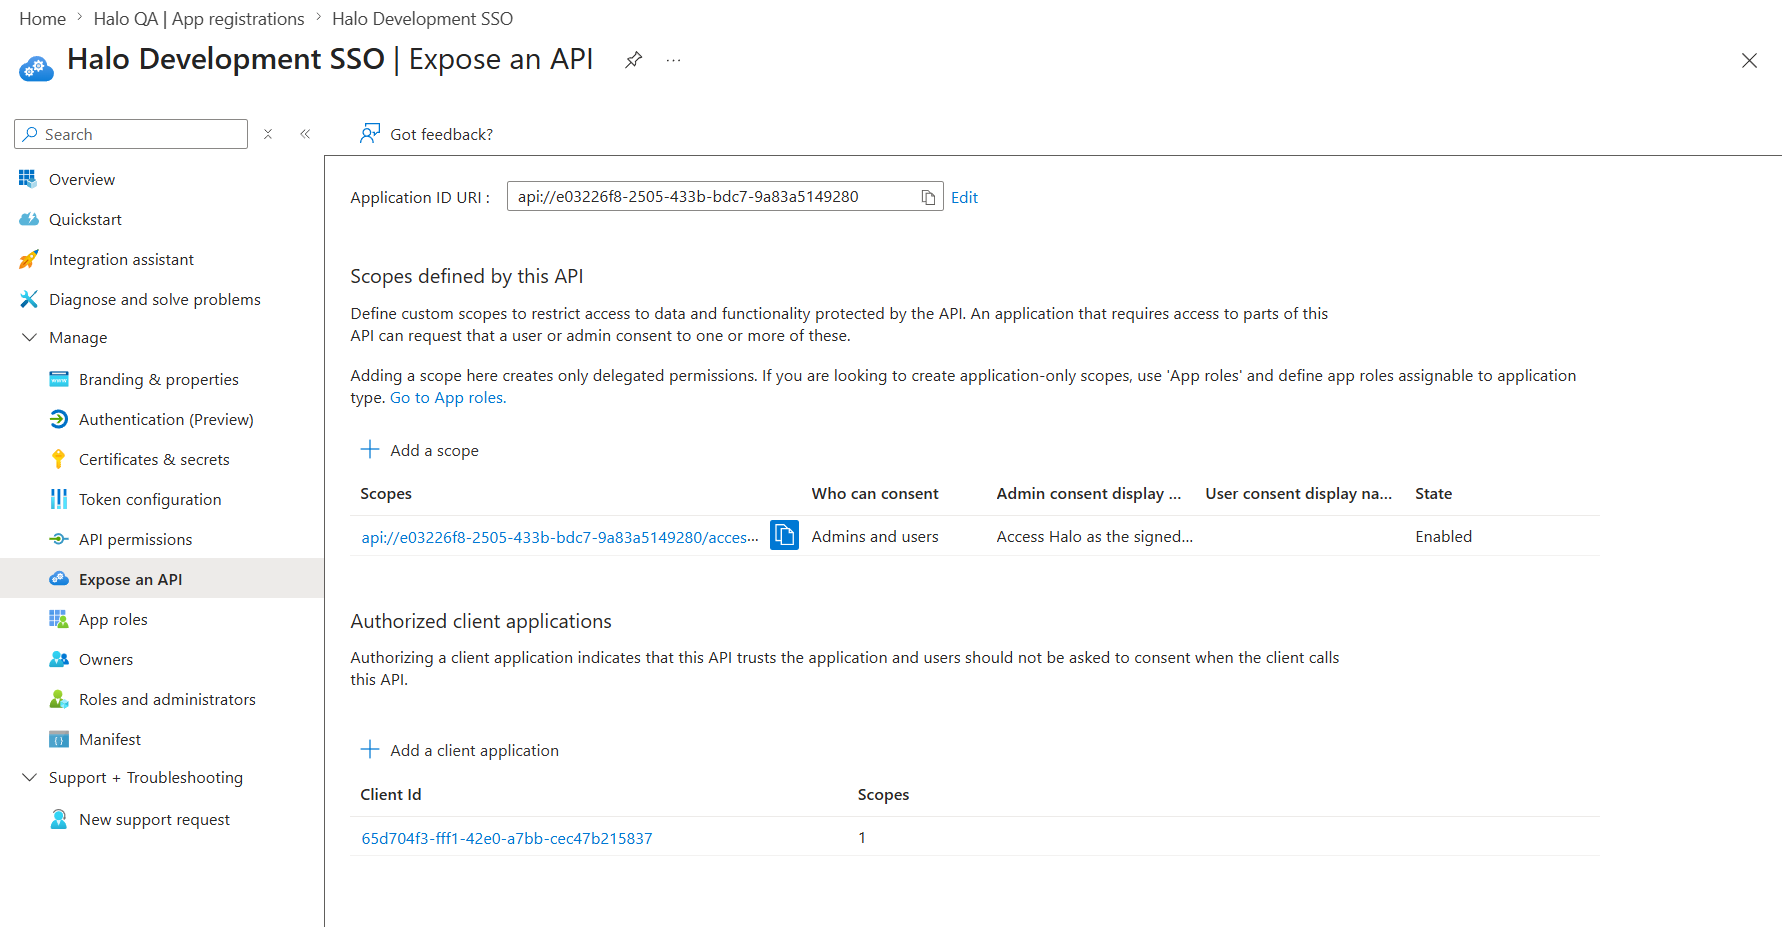
4.2 Expose an API on your SSO app registration
- In the Microsoft Entra admin center → Entra ID → App registrations, open your Halo SSO application.
- Under Manage → Expose an API.
- Confirm the Application ID URI. By default, Entra proposes
api://{your-sso-app-client-id}. Keep the default unless you have a reason to use a custom URI or you already have a custom URI configured (see §4.6). - Select Add a scope and create:
- Scope name:
access_as_user - Who can consent: Admins and users (or Admins only, per your policy)
- Display name/description: e.g. "Access Halo as a user"
- State: Enabled
- Scope name:
- Save. The full scope string is the Application ID URI +
/access_as_user.
If you changed the Application ID URI from the default, you must also set the matching value in Halo (§5.4).
4.3 Authorise the Halo Mobile app as a client
Still under Expose an API, in Authorized client applications:
- Select Add a client application.
- Client ID:
65d704f3-fff1-42e0-a7bb-cec47b215837(the Halo Mobile app - a multi-tenant app published in Halo's own tenant). - Tick the
access_as_userscope you created. - Add application.
This pre-authorises the mobile app so your users aren't prompted to consent to the scope individually.
4.4 Set requestedAccessTokenVersion/accessTokenAcceptedVersion to 2
- In the SSO application, open Manifest.
- In the Microsoft Graph App Manifest, ensure the requestedAccessTokenVersion is set to 2. This may not show, and you may only have access to the AAD Graph App Manifest; in which case proceed to step 3.
- In the Microsoft Graph App Manifest, ensure the accessTokenAcceptedVersion is set to 2. This may not show, and you may only have access to the Microsoft Graph App Manifest.
- Save.
4.5 Grant admin consent
The Halo Mobile app requests the delegated permissions User.Read and
DeviceManagementManagedApps.ReadWrite (the latter allows the app to enrol
itself for Intune App Protection). These typically require tenant admin
consent.
- Grant consent from Entra ID → Enterprise applications → Halo Mobile → Permissions → Grant admin consent, or
- Use the consent link Halo provides on the Advanced Settings page in the "Mobile App" section.
4.6 Application ID URI - default vs custom
- Default (
api://{client-id}): nothing extra to do. - Custom (e.g. a verified-domain URI): whatever you set here must match what Halo validates against. Set the matching Application ID URI value in the Single Sign-On record in Halo.
4.7 Reference - Halo Mobile app identifiers
| Item | Value |
|---|---|
| Halo Mobile app (client id) | 65d704f3-fff1-42e0-a7bb-cec47b215837 |
| App bundle / package id | com.haloservicesolutions |
| Delegated permissions | User.Read, DeviceManagementManagedApps.ReadWrite |
5. Halo configuration
All under Config → Advanced Settings except §5.4.
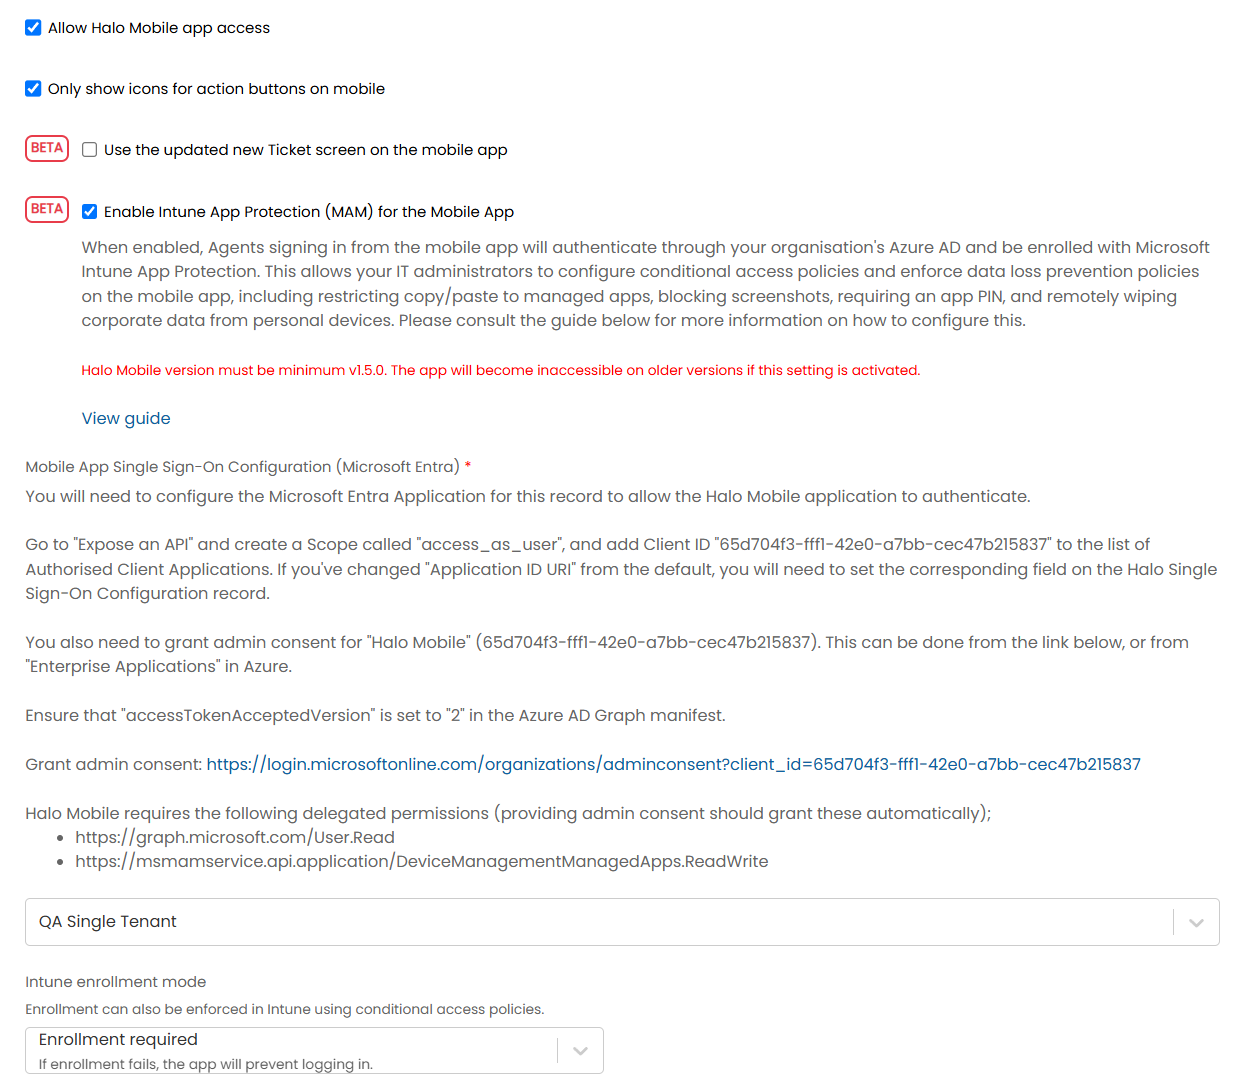
5.1 Enable Intune App Protection (MAM) for the Mobile App
Turns on the Intune-protected sign-in flow for your instance. When enabled (and an SSO record is selected, §5.2), the app stops using the standard authorization-code flow and routes through Intune.
Note: enabling this locks out older app versions that don't support the new flow.
5.2 Mobile app single sign-on configuration
Select which Entra Single Sign-on record the mobile app should use for its MSAL sign-in. The app takes the client id and tenant id from this record.
5.3 Intune enrolment mode
- Required - in-app gate: users cannot sign in until Intune enrolment succeeds.
- Optional - enrolment is attempted; if it fails, the user is still allowed in (with messages shown in some cases).
Conditional Access (§9), if configured, overrides this and makes enrolment mandatory regardless. Use this setting as a fallback where CA isn't in place.
Note that a MAM policy targeting the agents using the mobile app will need to be configured if setting enrollment to required.
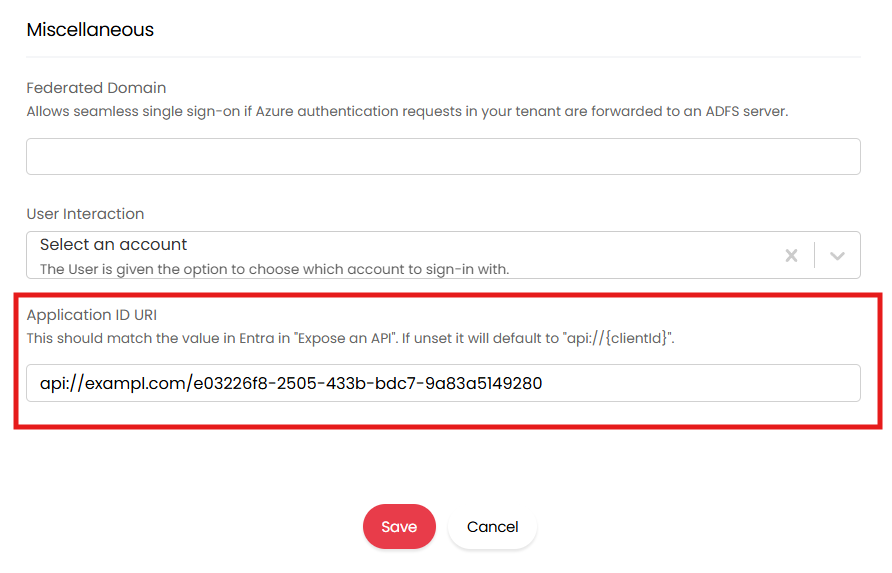
5.4 Application ID URI (only if you customised it in §4.6)
Set this to match the custom Application ID URI on your SSO app registration.
Leave blank to use the Entra default (api://{client-id}). This is found on the Single Sign-On configuration record in "Config > Integrations > Single Sign-On".
5.5 What the app reads
For reference, /api/InstanceInfo exposes the resulting settings to the app:
mobileapp_enable_mam, mobileapp_azure_tenant_id, mobileapp_api_scope
(api://.../access_as_user), and mobileapp_intune_enrollment_mode.
6. MDM vs MAM (what they are)
- MAM (Mobile Application Management) / App Protection Policies (APP) protects the app's data only - PIN, copy/paste and screenshot controls, selective wipe - without managing the device. Ideal for BYOD. This is the primary Intune feature for the Halo app.
- MDM (Mobile Device Management) manages the whole device (device enrolment via Company Portal). Needed only if you want device-wide control, managed-config auto-connect, or device-compliance Conditional Access.
You can use MAM alone, MDM alone, or both. Most organisations protecting Halo on personal devices want MAM.
7. Intune App Protection (MAM) setup
7.1 Prerequisites
- Licensing: Intune Plan 1 (or a suite that includes it) with MAM capability. Device-only licences do not support App Protection Policies. Your Halo agents that log into the Mobile app will require an Intune licence.
- Admin role: Intune Administrator / Global Administrator (or an Application Manager RBAC role with Managed-apps permissions).
- Broker app on the device (see §10): Company Portal (Android) / Microsoft Authenticator (iOS). Enrolment requires the broker.
7.2 Create App Protection Policies
Create one policy per platform:
- In the Microsoft Intune admin center → Apps → Protection (a.k.a. App protection policies) → Create policy → choose iOS/iPadOS or Android.
- Basics: name (e.g.
Halo - iOS - APP) and description. - Apps: select the Halo app. You can add the Halo app to Intune by following §8.1 (required if you plan on using MDM) or add it as a custom app by bundle id/package name (
com.haloservicesolutions). - Data protection: configure DLP controls (cut/copy/paste, save-as, "send org data to other apps", etc.).
- Access requirements: PIN, biometrics, credentials.
- Conditional launch: min OS/app/SDK version, jailbreak/root checks, and the action on failure (block/wipe).
- Assignments: assign to the relevant user groups.
- Create.
App protection policies take time to apply and are delivered/refreshed on app check-in, so newly-set controls (clipboard, screenshots, PIN) may not be active immediately after first sign-in.
8. Intune MDM setup (optional)
Only needed for device-level management, managed-config auto-connect, or device-compliance CA.
8.1 Add the Halo app to Intune
Add the Halo app in Intune > Apps;
- iOS: add the App Store app (and assign it); the Halo bundle id is
com.haloservicesolutions. - Android: add via Managed Google Play; app id
com.haloservicesolutions.
8.2 Device enrolment
Enrol devices via Company Portal (Android Enterprise / iOS Automated or Device Enrolment). See Microsoft documentation on how to configure this.
8.3 Auto-connect via managed config ( halo_url )
You can pre-set and lock the Halo URL so the app skips the "enter your Halo URL" screen.
- Important: this uses the Managed devices app configuration channel, which requires an MDM-enrolled device. It does not work through the MAM-only channel. BYOD/MAM-only users type the URL as normal.
- Console: Apps → Configuration → Create → Managed devices, one policy
per platform, targeting the Halo app, with key
halo_url= your Halo URL (e.g.https://mycompany.haloitsm.com).
When this is set, the "Enter your Halo URL" screen will not show, and it will instead show a "Connecting to Halo" screen and auto-connect to the Halo instance specified.
9. Conditional Access (optional, recommended)
Conditional Access (CA) is the Microsoft-native way to enforce that the app is protected before it can obtain a token.
9.1 What it does here
With a "Require app protection policy" CA policy in place, Entra will not issue a token to the app until it is enrolled and protected. The app detects this and drives the user through Intune enrolment automatically, then completes sign-in.
9.2 Create the policy
- Microsoft Intune admin center → Endpoint security → Conditional access → Create new policy (or via Entra ID → Conditional Access).
- Users: target the relevant users/groups.
- Target resources: the cloud app(s) the policy protects. The target for this is your Halo SSO app (not the Halo Mobile application).
- Conditions: set Device platforms (iOS, Android).
- Grant → Require app protection policy.
- Enable and create.
App Protection Policies (§7) must exist and be assigned before turning this on, or users will be blocked. App Protection Policies take time to apply.
9.3 Device-compliance CA - caveat
A CA policy that requires a compliant / managed device ("Require device to be marked as compliant" / hybrid-joined) cannot be satisfied by MAM app protection - the device itself must be MDM-enrolled via Company Portal. The Halo app detects this case and tells the user to enrol their device; it cannot do it for them. Only use device-compliance CA if you're running full MDM.
9.4 Conditional Access vs Halo enrolment mode
| Setting | Enforcement point | Notes |
|---|---|---|
| CA "Require app protection policy" | Microsoft Entra | Recommended. Robust; overrides Halo enrolment mode. |
| Halo enrolment mode = Required | Halo app | Fallback where CA isn't configured. |
| Halo enrolment mode = Optional | Halo app | Attempts enrolment; allows access if it fails. |
10. Broker apps (Company Portal / Microsoft Authenticator)
Intune enrolment and CA remediation require a Microsoft broker app on the device:
- Android: Intune Company Portal.
- iOS: Microsoft Authenticator.
Without the broker, sign-in may fall back to the browser but enrolment cannot complete. If a user is missing it, the app prompts them to install the correct one from the store. Consider deploying the broker to users in advance.
11. Troubleshooting (admin-facing)
| User sees | Likely cause | Fix |
|---|---|---|
| "Needs admin approval" at sign-in | Admin consent not granted (§4.5). | Grant tenant admin consent for Halo Mobile. |
| "Install Company Portal / Microsoft Authenticator" | Broker app missing. | Install the correct broker (§10). |
| No Intune licence / not licensed | User has no Intune licence, or no APP assigned. | Assign an Intune licence and an App Protection Policy. |
| Enrolment/setup not completed by your organisation | "Expose an API" / client authorisation/consent incomplete (§4). | Recheck §4.2–4.5. |
| Device must be enrolled (compliance) | Device-compliance CA in place; device not MDM-enrolled. | User enrols device via Company Portal, or relax the CA (§9.3). |
| "Sign in again - new policies" | Halo MAM/SSO settings changed since last sign-in. | Expected after config changes; user re-signs in. |
| Tenant mismatch error | Signed-in account isn't in the SSO tenant configured in Halo. | Confirm the SSO record/tenant (§5.2). |
| Unable to validate token | Token exchange failed, likely configuration not completed or Application ID URI doesn't match between Halo and Entra | Recheck §4.2–4.6. |
| Agent not found with Azure OID | The Entra user/tenant combo does not exist in Halo as an Agent account | Run an Entra sync for the tenant, and sync Entra users to Halo agent accounts. Verify the agent can log into the Web application with Entra SSO. |
12. Appendix
Glossary
- MDM - Mobile Device Management (whole-device management).
- MAM / APP - Mobile Application Management / App Protection Policy (app-data protection, no device enrolment).
- Conditional Access (CA) - Entra rules gating token issuance.
- Broker - Company Portal (Android) / Microsoft Authenticator (iOS).
- UPN / OID / Tenant ID - user principal name / Entra object id / directory id. User matching for the Halo exchange is by OID + tenant (UPN matching is disabled for multi-tenant security).
- Token exchange - the grant Halo uses to swap the Entra-issued token for a Halo session token.
Reference
| Item | Value |
|---|---|
| Halo Mobile app (client id) | 65d704f3-fff1-42e0-a7bb-cec47b215837 |
| App id (bundle/package) | com.haloservicesolutions |
| Delegated permissions | User.Read, DeviceManagementManagedApps.ReadWrite |
| Scope to expose | {Application ID URI}/access_as_user |
| Managed config key | halo_url |