CORS Policy on Halo API
- CORS
By default, the CORS policy on all Halo web apps is a wildcard that allows all.
To enable a stricter CORS policy to block requests from other origins, follow the below.
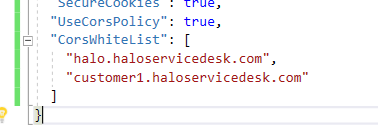
In appsettings.json in the API and Auth Server add "UseCorsPolicy": true.
Also, add "CorsWhiteList" as an array of strings. Enter the hostname of each origin you would like to be able to access. The web app and portal must be included in this list if they do not have the same origin as the API application otherwise they will be blocked.
E.G
NB. If customer is using 'localhost' (i.e. their instance is On-Prem for the local network, a port must be specified for it to work). Example localhost:443